Cybersecurity headlines are data-layer warnings.
Threat analysis, breach lessons, and Cyberstorage guidance for organizations defending unstructured data.
Latest
All threat briefs →Cyberstorage Explainer
How long do data breaches go undetected? What dwell time measures, and what it leaves out
October 2, 2026 • 6 min
Sector Spotlight
Government data breaches in 2026: a running list, and the patterns underneath it
October 1, 2026 • 6 min
Threat Brief
The Pentagon personnel breach: nine months of file access, and a scope still written as “may”
September 28, 2026 • 7 min
Practitioner Guide
When every storage product claims Cyberstorage: seven tests that tell them apart
September 23, 2026 • 6 min
New here? Start with these
Three pieces that explain the category, the mechanism, and the limit of the tools most organizations already own.
- 1
What Cyberstorage is, and why it exists
Cyberstorage builds security and recovery into the data storage layer itself. Here is what that means, the thirty-year assumption that made the category necessary, why Gartner named it in 2021, and how it differs from backup and traditional NAS.
7 min read
- 2
Ransomware protection at the storage layer: how it actually works
What real ransomware protection looks like at the layer attacks actually touch: the visibility, detection, policy, response, recovery, and evidence chain, explained link by link.
9 min read
- 3
Backup is necessary. It is not a security control.
Immutable backups matter. But a recovery copy cannot see an attack, cannot stop exfiltration, and cannot tell you that data was stolen. Treating backup as security leaves the live data undefended.
5 min read
Cyberstorage Explainers
Plain-language explanations of the architecture and the category.
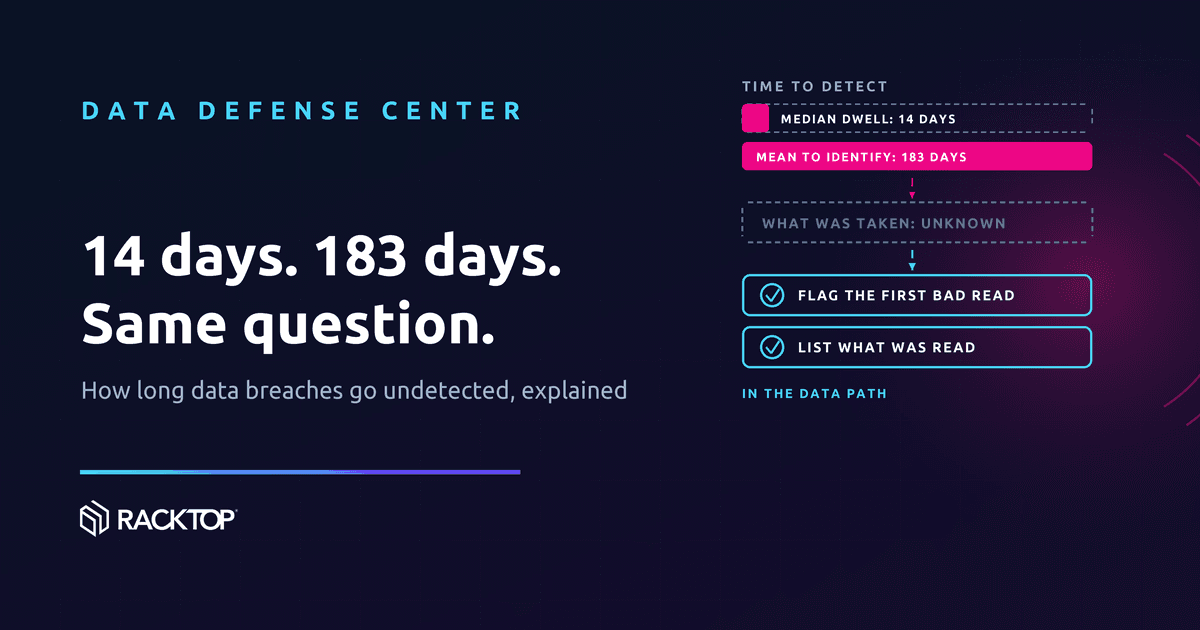
How long do data breaches go undetected? What dwell time measures, and what it leaves out
Mandiant puts the median dwell time at 14 days. IBM puts the average time to identify a breach at 183. Both are right, and neither says how long it takes to learn what an attacker took.
October 2, 2026
What Cyberstorage is, and why it exists
Cyberstorage builds security and recovery into the data storage layer itself. Here is what that means, the thirty-year assumption that made the category necessary, why Gartner named it in 2021, and how it differs from backup and traditional NAS.
July 12, 2026
Ransomware protection at the storage layer: how it actually works
What real ransomware protection looks like at the layer attacks actually touch: the visibility, detection, policy, response, recovery, and evidence chain, explained link by link.
July 12, 2026
Practitioner Guides
Hands-on guidance for storage, security, and SOC teams.

When every storage product claims Cyberstorage: seven tests that tell them apart
Gartner expects every storage product to include Cyberstorage capabilities by 2029. When the label is universal, a datasheet stops telling buyers anything. Seven live tests for a proof of concept still can.
September 23, 2026
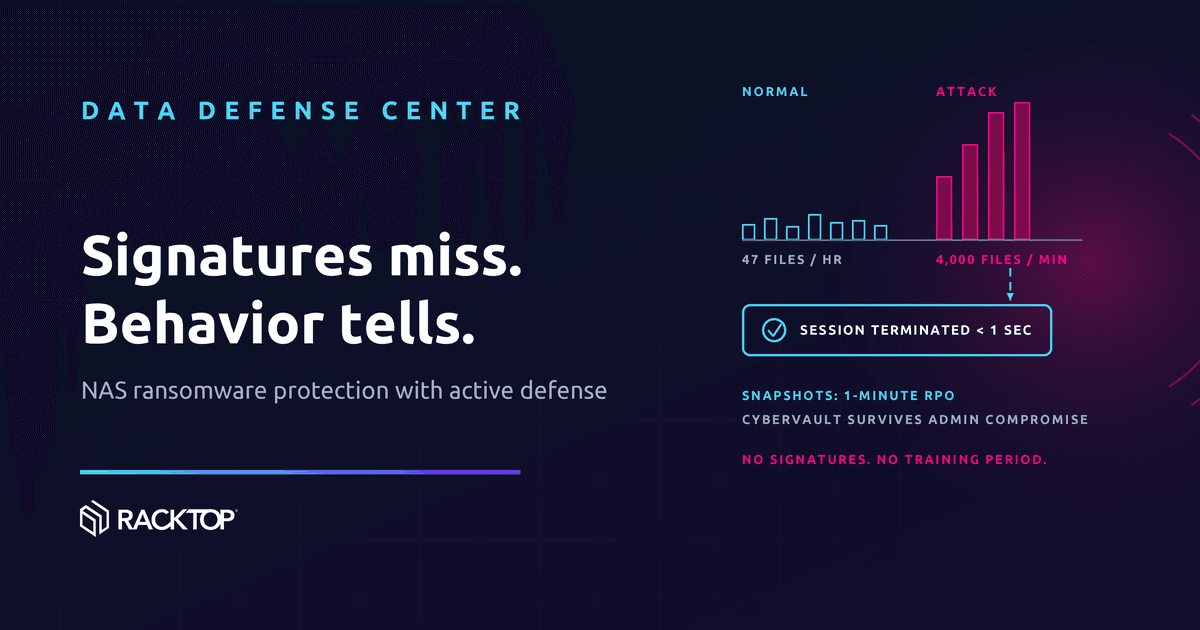
NAS ransomware protection: catch the attack by how it behaves
Real NAS ransomware protection is not a signature list or a nightly backup. It is user behavior analytics on every file operation, active defense that terminates a hostile session in under a second, and a cybervault that survives even administrative compromise.
August 9, 2026
File activity telemetry: what your SOC actually needs from storage
Most NAS audit feeds were designed for compliance checkboxes, not threat detection. Here is what detection-grade file activity telemetry looks like, how to wire it into SIEM and SOAR workflows without drowning the license, and the two tests that prove the integration is real.
June 30, 2026
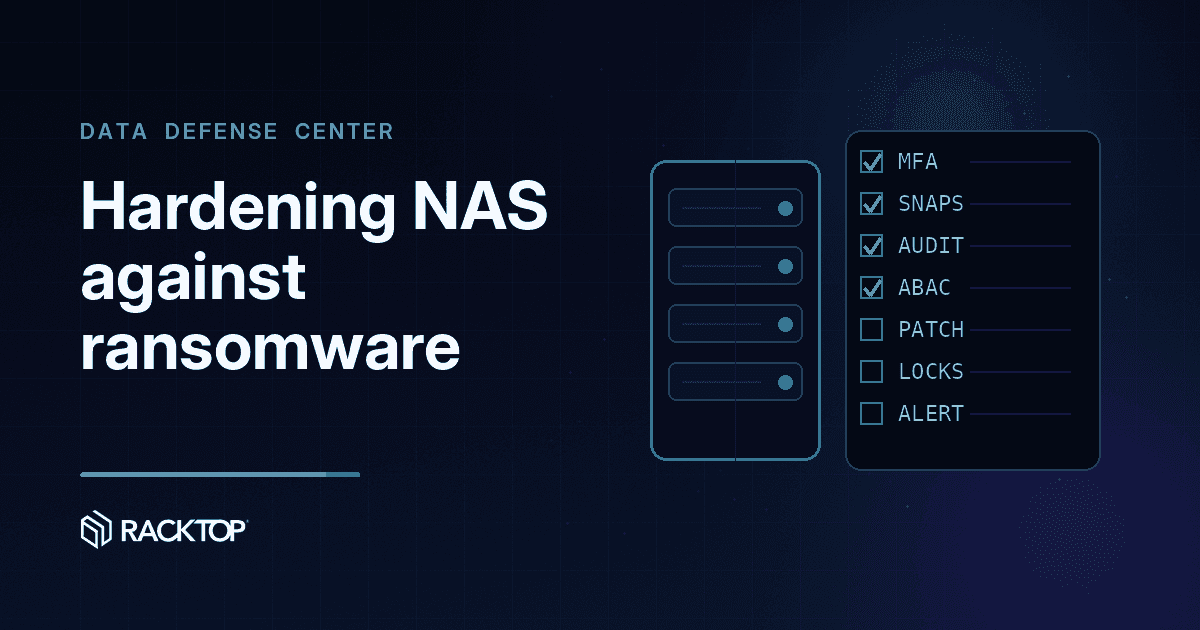
Hardening NAS against ransomware: a practitioner checklist
A working checklist for storage and security teams: seven areas to verify on your file infrastructure so an attack on a share is detected and contained in progress, not just recovered from later.
May 20, 2026
Executive Briefings
Board-level framing of unstructured-data risk and resilience.
Recovery time is now a disclosure question
Regulators, insurers, and customers increasingly ask the same two questions after an incident: how fast were you back, and what exactly was taken? Both answers are determined at the data layer, before the incident ever happens.
June 30, 2026
A board-level view of unstructured data risk
Most of an organization’s data is unstructured files, and most of its risk concentrates there. A short briefing for executives on why the storage layer belongs on the risk register.
May 28, 2026
Federal & Defense Notes
Zero Trust, classification, and mission-data guidance for government.
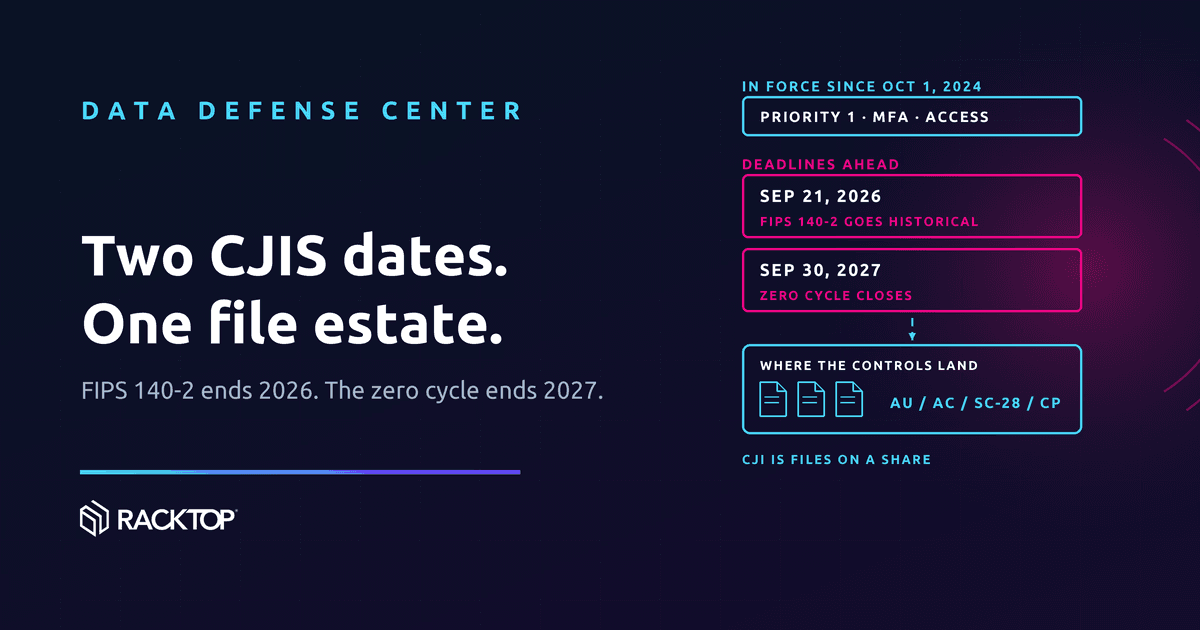
CJIS Security Changes for 2026 and 2027: What State and Local Agencies Need to Know
Two dates now shape CJIS planning for state and local agencies: the FIPS 140-2 sunset on September 21, 2026, and the end of the zero-cycle period on September 30, 2027. Here is what each one actually requires, and why so much of the work lands on storage.
August 21, 2026
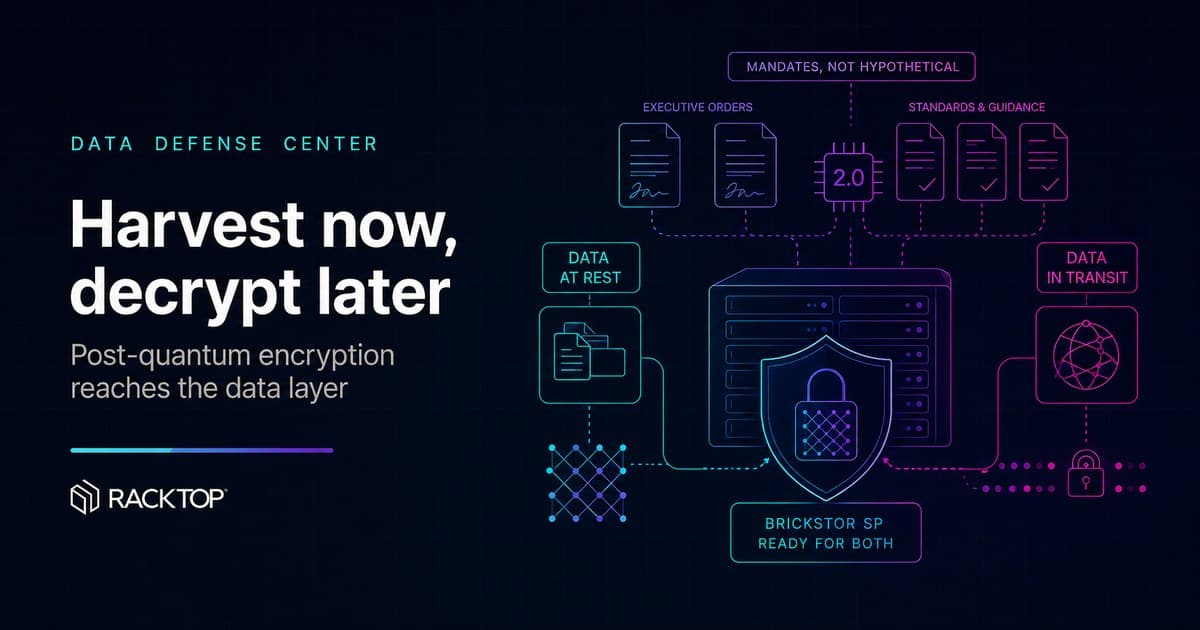
Harvest now, decrypt later: post-quantum encryption reaches the data layer
Two executive orders, three NIST standards, and NSA’s CNSA 2.0 have turned post-quantum cryptography from research topic into procurement requirement. What the mandates actually say, and how BrickStor SP is post-quantum ready for data at rest and data in transit.
July 27, 2026
Sharing without surrender: NATO’s data strategy and the storage layer
NATO’s Data Strategy for the Alliance sets a 2030 target: federated data sharing across the Alliance while every ally keeps control of its own data. Sharing and sovereignty at once is not a networking problem. It is a mandate for enforcement that lives where the data lives.
July 17, 2026
Zero Trust reaches the data pillar
What Zero Trust security is, where it came from, and how the CISA and DoD Zero Trust Maturity Models differ, who each applies to, and why both converge on the data pillar.
July 12, 2026
Healthcare, Critical Infrastructure & Enterprise IT
Sector-specific data-defense pressures and lessons.
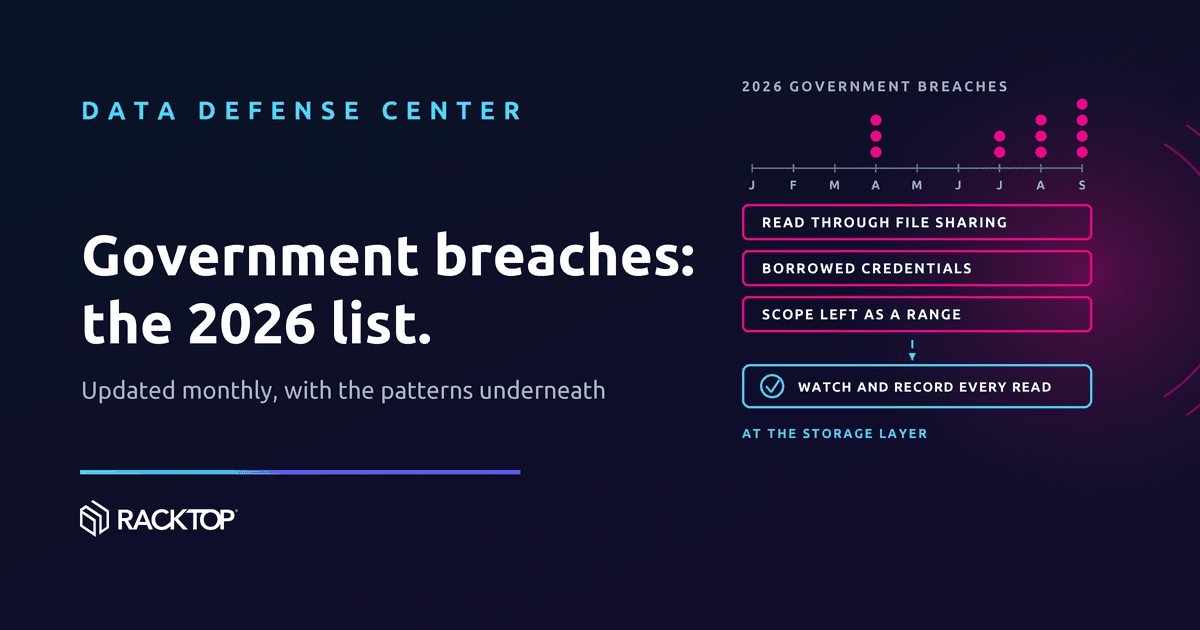
Government data breaches in 2026: a running list, and the patterns underneath it
A running list of notable 2026 government data breaches, from county networks to the FBI and the Pentagon, updated monthly, with the patterns that repeat across them.
October 1, 2026
Why healthcare keeps paying the highest breach costs
Healthcare has carried the highest average breach cost of any industry for more than a decade. The five reasons why trace back to the data itself: sensitive, regulated, sprawling, and largely unstructured.
July 12, 2026
Critical infrastructure’s quiet exposure: the IT file share
Utilities invest heavily in OT security while the IT side (engineering diagrams, SCADA documentation, customer data on ordinary file servers) remains the softer target attackers actually take.
July 12, 2026
RackTop Perspective
Points of view from the team that pioneered Cyberstorage.
The archive keeps the risk. It loses the controls.
Tiering data to cheaper storage changes what it costs to keep. It does not change what it costs to lose. Archived files keep every property that made them sensitive and usually shed the monitoring, access control, and audit that protected them.
September 8, 2026
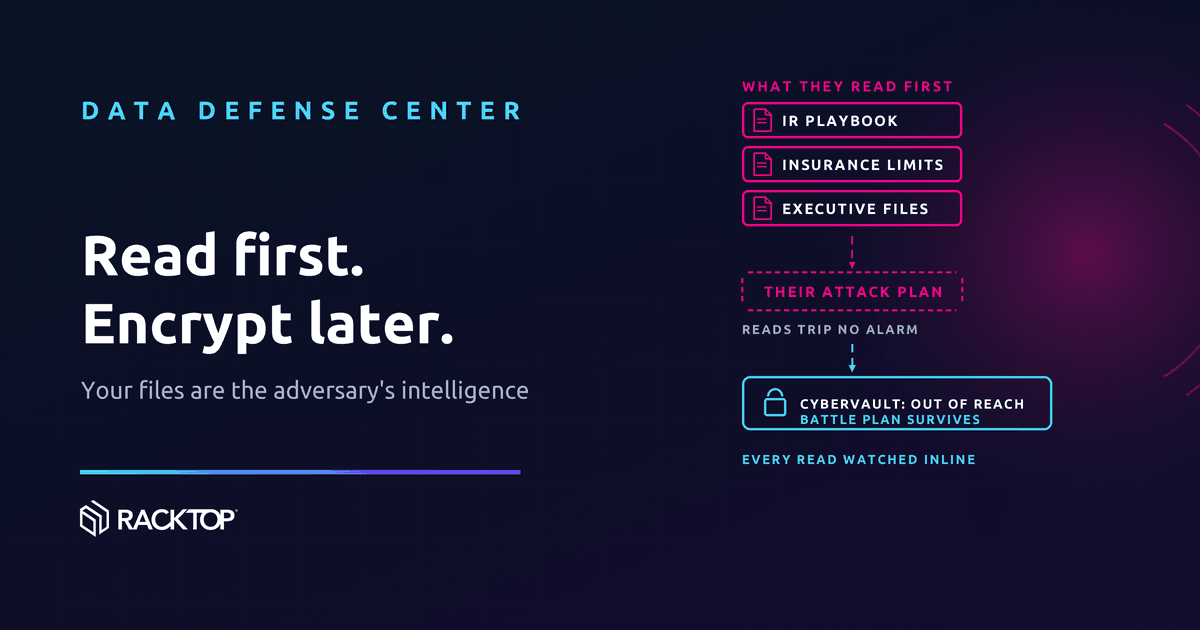
Before the ransom note: what hackers learn from your files
Ransomware is the loudest threat to unstructured data, but it is not the first one. Hackers and APTs read your files long before they encrypt anything, and what they learn shapes the entire attack. Cyberstorage exists because protection has to start at the read, not the ransom note.
August 9, 2026
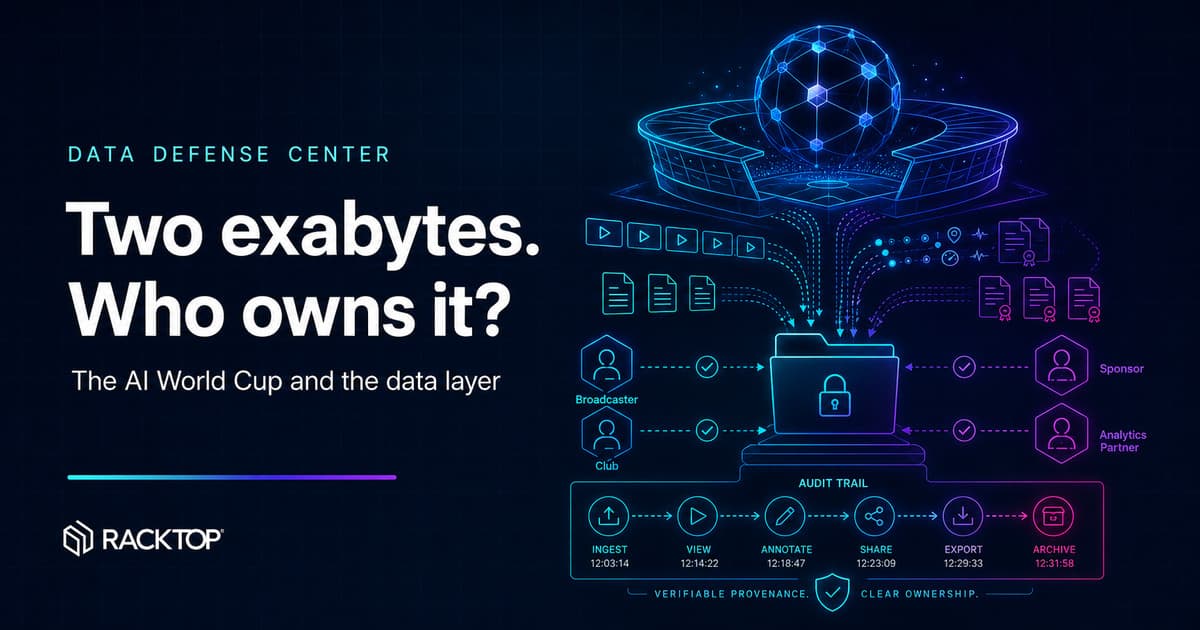
Two exabytes, and no one agrees who owns it: the AI World Cup and the data layer
The 2026 World Cup is projected to generate roughly 90 petabytes of tournament data, and some two exabytes overall. Almost none of it is rows in a database. The harder problem is not storing it: ownership is a bundle of contractual rights, and only the data layer can prove who actually touched what.
July 14, 2026
Backup is necessary. It is not a security control.
Immutable backups matter. But a recovery copy cannot see an attack, cannot stop exfiltration, and cannot tell you that data was stolen. Treating backup as security leaves the live data undefended.
July 12, 2026
Latest Threat Briefs
Analysis of active threats and what they mean for data at the storage layer.
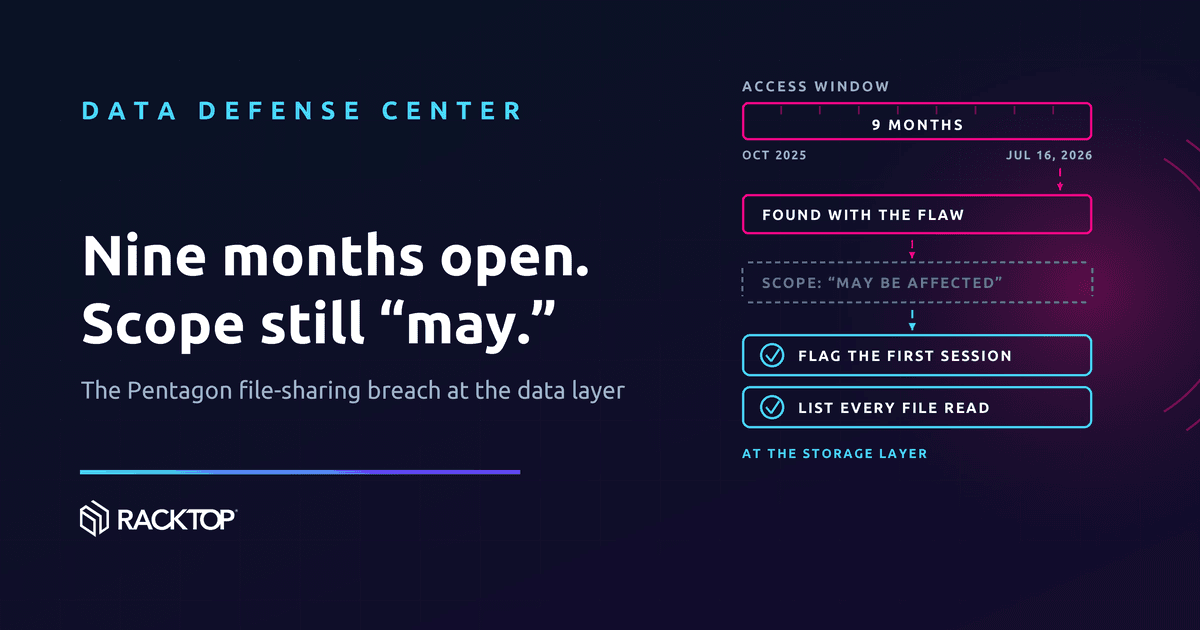
The Pentagon personnel breach: nine months of file access, and a scope still written as “may”
Unauthorized users accessed unencrypted military personnel files on a Defense Manpower Data Center file-sharing system for nine months before the flaw was found. The notice to victims does not say how many people were affected.
September 28, 2026

No malware, no lateral movement, and every document copied anyway
A phone call to an executive, a stolen session token, and a bulk sweep of SharePoint, OneDrive, Exchange, and Box. Researchers found no malware and no lateral movement in the campaign, which leaves the reads as the only thing left to detect.
September 8, 2026

The reporting tool was a copy of everyone
The system breached at Mathspace was not the product. It was the internal reporting tool sitting behind it, holding a standing read view of more than a million students, staff, and parents.
September 8, 2026
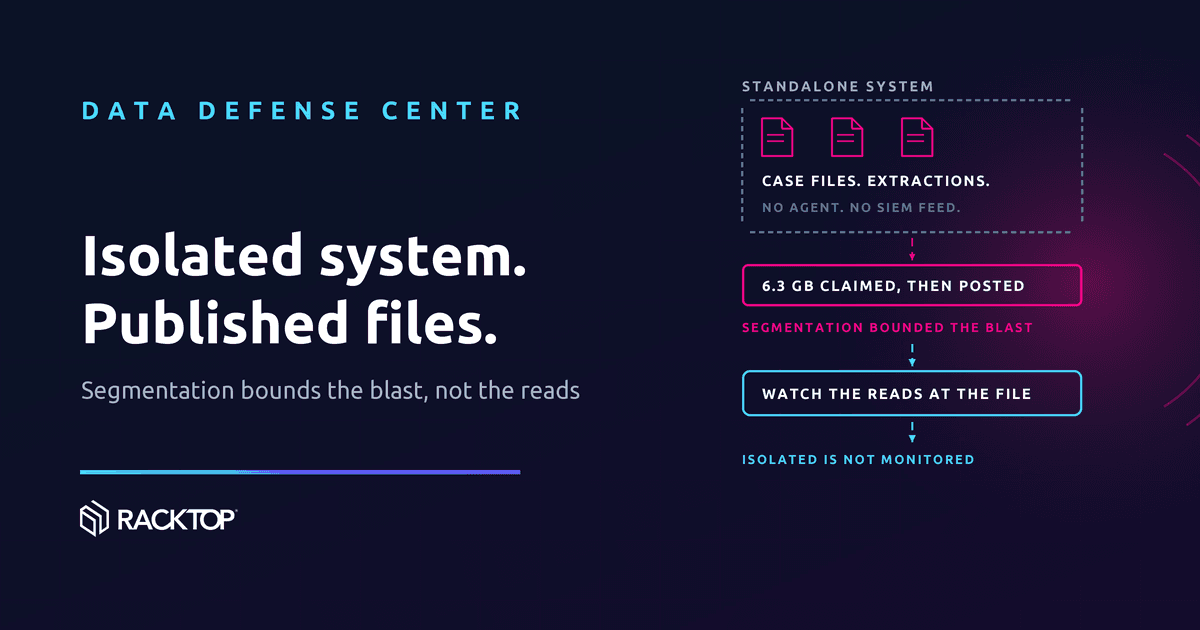
Isolation contained the incident. It did not protect the files.
A standalone ATF system, wired to nothing else, still held the case folders a ransomware group published. Segmentation bounded the intrusion. It never watched the files.
September 2, 2026
Looking for datasheets, validations, and case studies? Visit the Resource Library →
See data-layer defense in your environment
In a 30-minute demo we’ll show Active Defense stopping an attack inline, immutable recovery, and surgical rollback — mapped to your data and your threats.