Topic · 15 articles
Compliance
CMMC, CJIS, CUI, and the control frameworks that land on storage.
Spans Federal & Defense, Practitioner Guide, RackTop Perspective, Sector Spotlight and Executive Briefing.
Labels you can enforce: a manager’s guide to metadata hygiene for Zero Trust, ACP 240, and STANAG
Zero Trust and coalition data sharing both depend on one thing most programs underfund: accurate labels on files. What the standards expect, where labels usually go wrong, and the questions a program manager should be asking.
7 min read
Body-worn camera storage: retention, chain of custody, and CJIS
Body-worn camera video is the largest and fastest-growing data set most departments own. Here is how to store it for years, prove who touched each file, keep it inside CJIS controls, and get it back after a ransomware attack.
7 min read
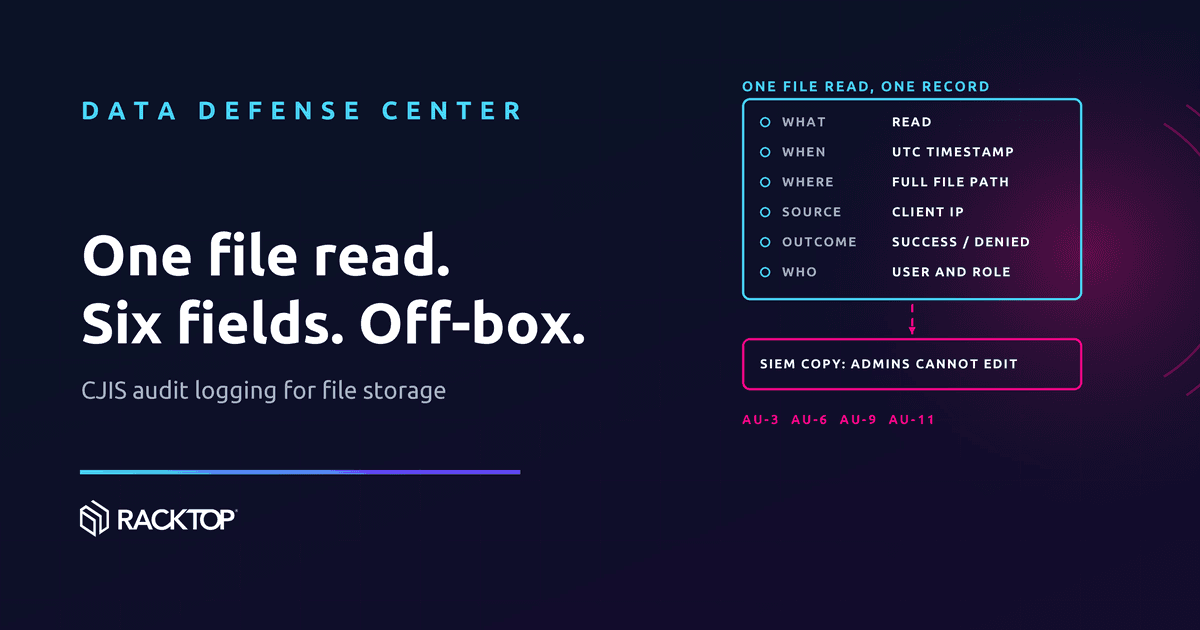
CJIS audit logging requirements for file storage
The CJIS audit controls read directly against the storage holding CJI. Here is what each one asks for, what an auditor will want to see, and where file shares usually fall short.
6 min read
CJIS storage checklist: 15 questions for any vendor holding your CJI
No storage product is CJIS certified, so a vendor’s CJIS page tells you little. These fifteen questions turn the CJIS v6.1 controls into answers you can check, and we answer every one of them for BrickStor SP.
3 min read
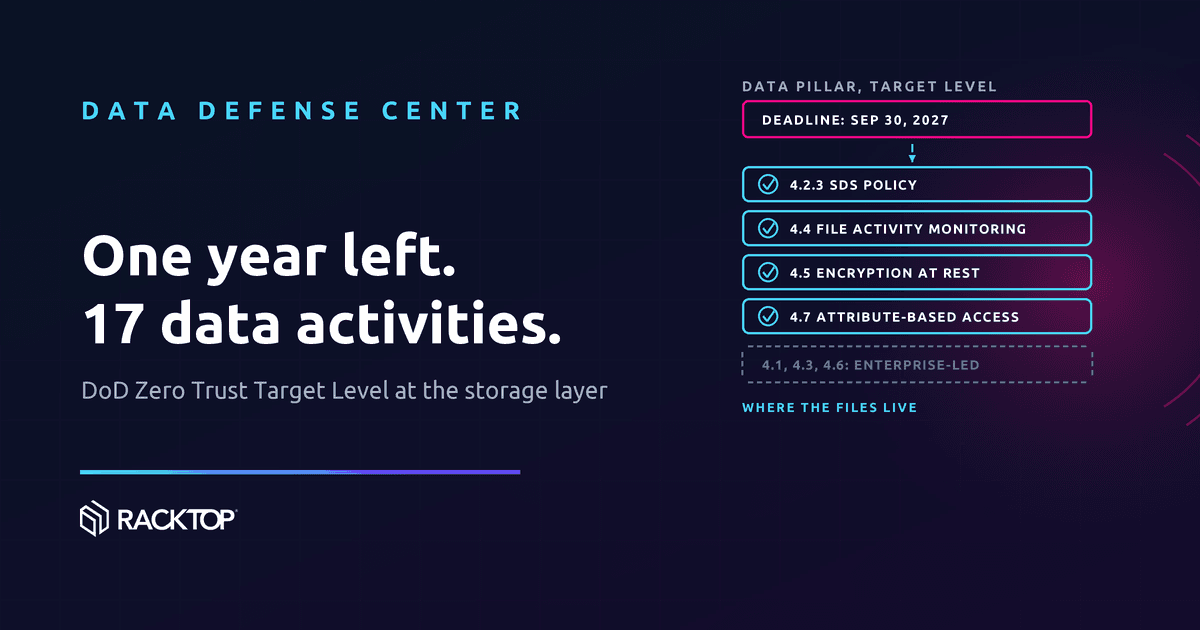
FY2027 is here: what the DoD Zero Trust data pillar requires, and what storage has to prove
Fiscal 2027 began October 1, the last year components have to reach Target Level Zero Trust. Seventeen of the 91 Target activities sit in the data pillar, and several of them land on storage.
6 min read
The archive keeps the risk. It loses the controls.
Tiering data to cheaper storage changes what it costs to keep. It does not change what it costs to lose. Archived files keep every property that made them sensitive and usually shed the monitoring, access control, and audit that protected them.
8 min read
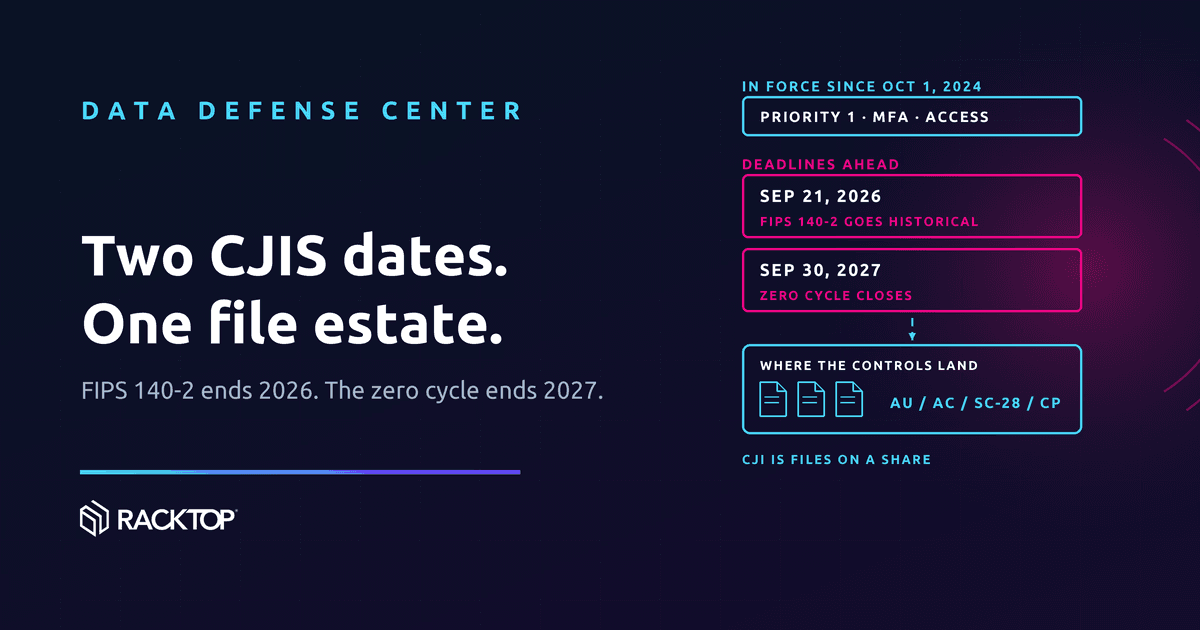
CJIS Security Changes for 2026 and 2027: What State and Local Agencies Need to Know
Two dates shape CJIS planning for state and local agencies: the FIPS 140-2 sunset, which took effect on September 22, 2026, and the end of the zero-cycle period on September 30, 2027. Here is what each one actually requires, and why so much of the work lands on storage.
11 min read
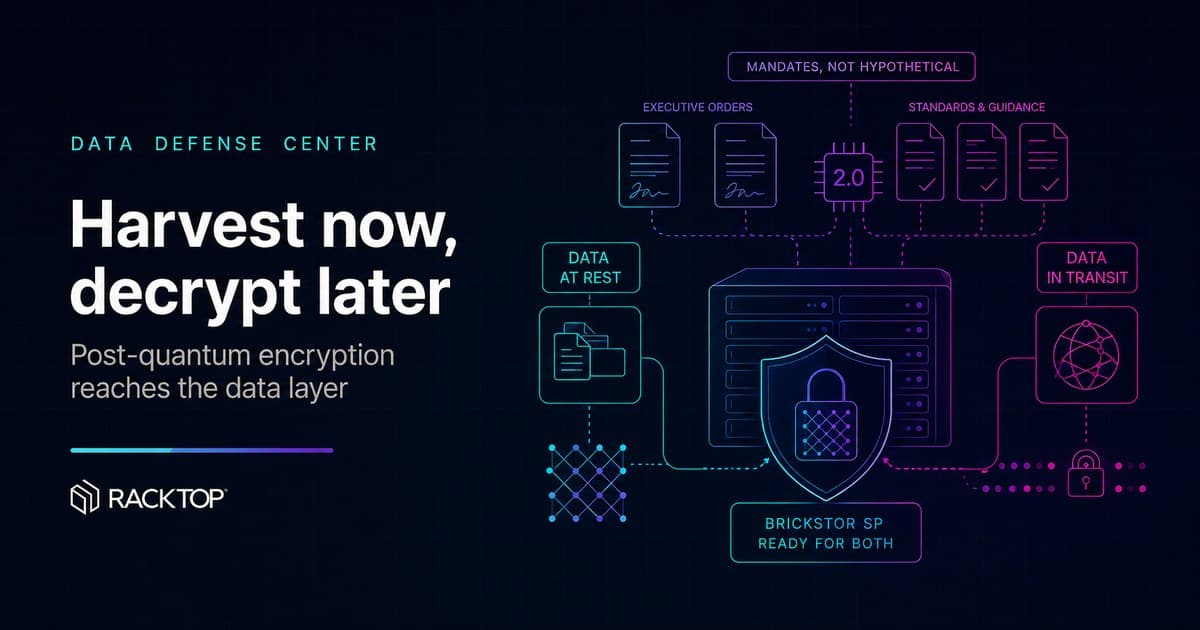
Harvest now, decrypt later: post-quantum encryption reaches the data layer
Two executive orders, three NIST standards, and NSA’s CNSA 2.0 have turned post-quantum cryptography from research topic into procurement requirement. What the mandates actually say, and how BrickStor SP is post-quantum ready for data at rest and data in transit.
6 min read
Sharing without surrender: NATO’s data strategy and the storage layer
NATO’s Data Strategy for the Alliance sets a 2030 target: federated data sharing across the Alliance while every ally keeps control of its own data. Sharing and sovereignty at once is not a networking problem. It is a mandate for enforcement that lives where the data lives.
6 min read
Zero Trust reaches the data pillar
What Zero Trust security is, where it came from, and how the CISA and DoD Zero Trust Maturity Models differ, who each applies to, and why both converge on the data pillar.
9 min read
Why healthcare keeps paying the highest breach costs
Healthcare has carried the highest average breach cost of any industry for more than a decade. The five reasons why trace back to the data itself: sensitive, regulated, sprawling, and largely unstructured.
6 min read
CUI lives in files. Protect it there.
Controlled Unclassified Information is overwhelmingly unstructured: drawings, specs, contract documents on file shares. CMMC compliance increasingly comes down to whether you can label, control, and account for those files, which is exactly what data labeling and ABAC at the storage layer deliver.
7 min read
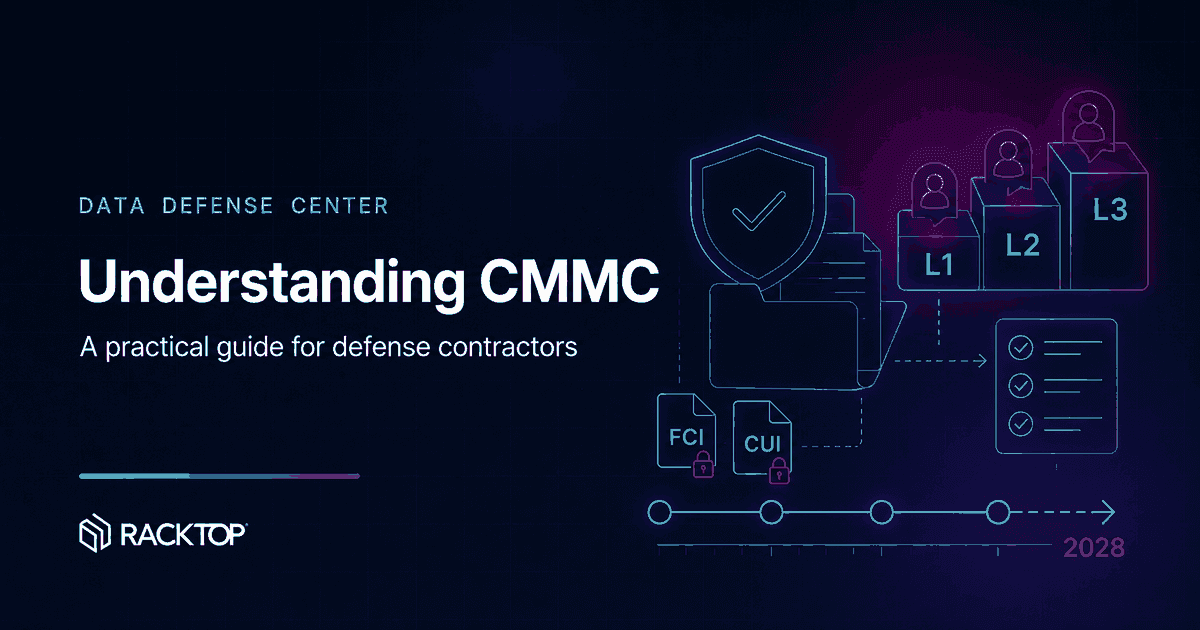
Understanding CMMC: A Practical Guide for Defense Contractors
What CMMC is, who must comply, the three levels, the phased enforcement timeline through 2028, and the path to certification for defense contractors handling FCI and CUI.
10 min read
Recovery time is now a disclosure question
Regulators, insurers, and customers increasingly ask the same two questions after an incident: how fast were you back, and what exactly was taken? Both answers are determined at the data layer, before the incident ever happens.
2 min read
A board-level view of unstructured data risk
Most of an organization’s data is unstructured files, and most of its risk concentrates there. A short briefing for executives on why the storage layer belongs on the risk register.
2 min read
See data-layer defense in your environment
In a 30-minute demo we’ll show Active Defense stopping an attack inline, immutable recovery, and surgical rollback — mapped to your data and your threats.