Topic · 11 articles
Cyber Recovery
Immutability, surgical restore, and recovery to a known trusted state.
Spans Threat Brief, Practitioner Guide, RackTop Perspective, Cyberstorage Explainer and Executive Briefing.
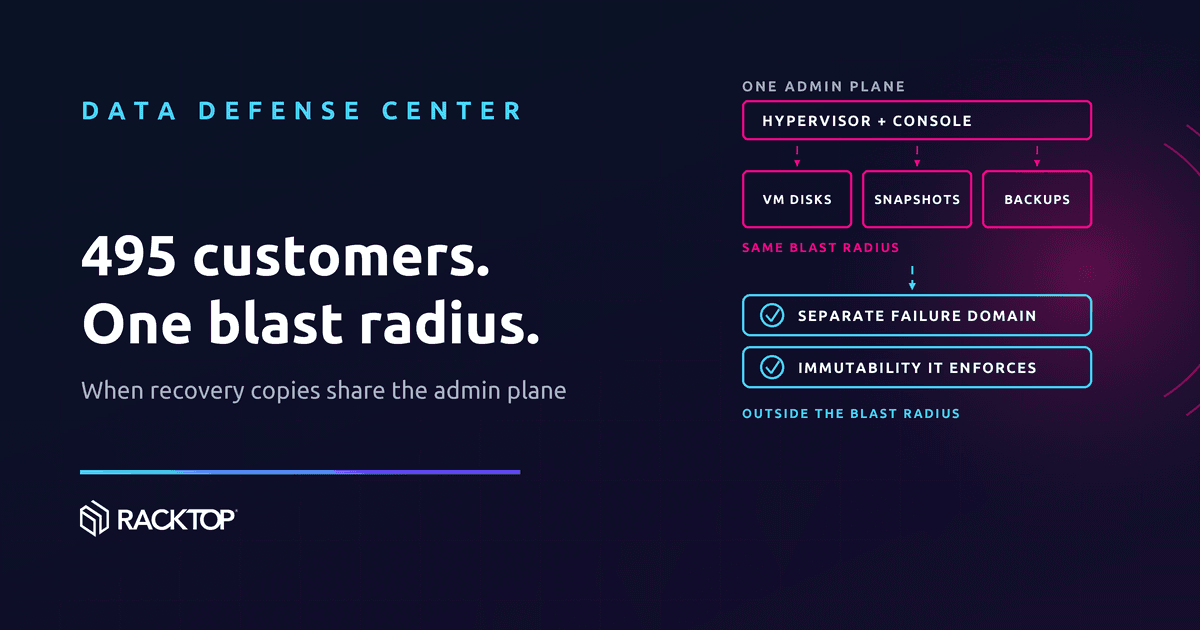
When ransomware takes the snapshots too: the IDCF Cloud attack, and how to keep recovery copies out of reach
Ransomware shut down servers for 495 customers of a Japanese cloud service, and the provider told them to rebuild from their own backups. Here is how RackTop deploys BrickStor SP so the data, and every copy of it, sits outside the attacker’s reach.
6 min read

When every storage product claims Cyberstorage: seven tests that tell them apart
Gartner expects every storage product to include Cyberstorage capabilities by 2029. When the label is universal, a datasheet stops telling buyers anything. Seven live tests for a proof of concept still can.
6 min read
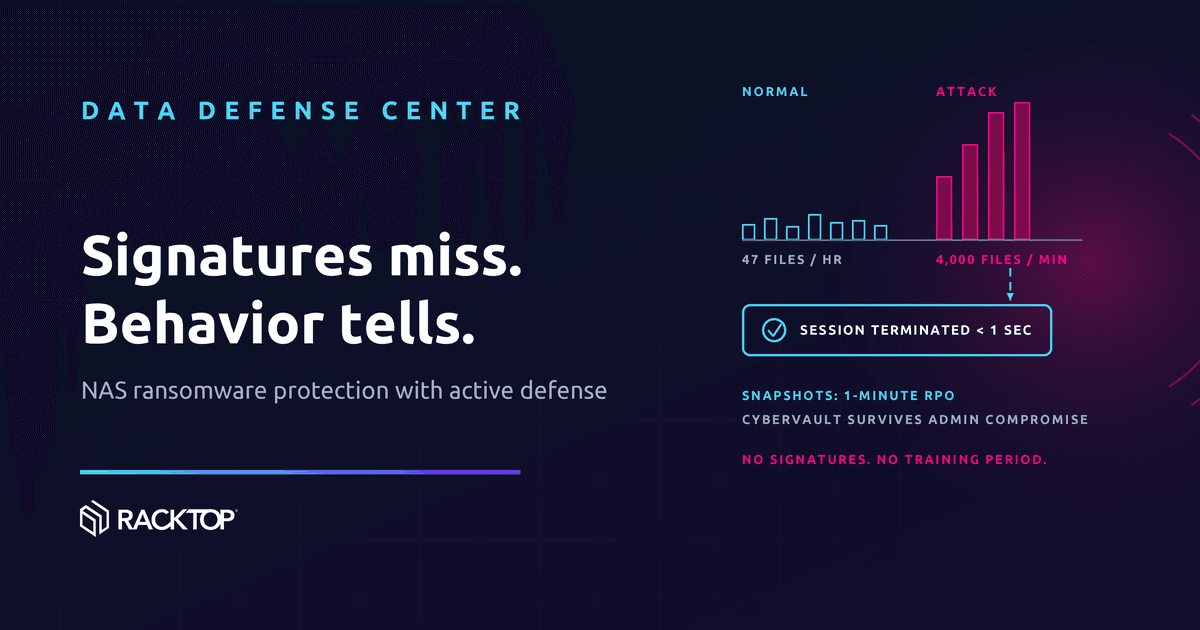
NAS ransomware protection: catch the attack by how it behaves
Real NAS ransomware protection is not a signature list or a nightly backup. It is user behavior analytics on every file operation, active defense that terminates a hostile session in under a second, and a cybervault that survives even administrative compromise.
5 min read
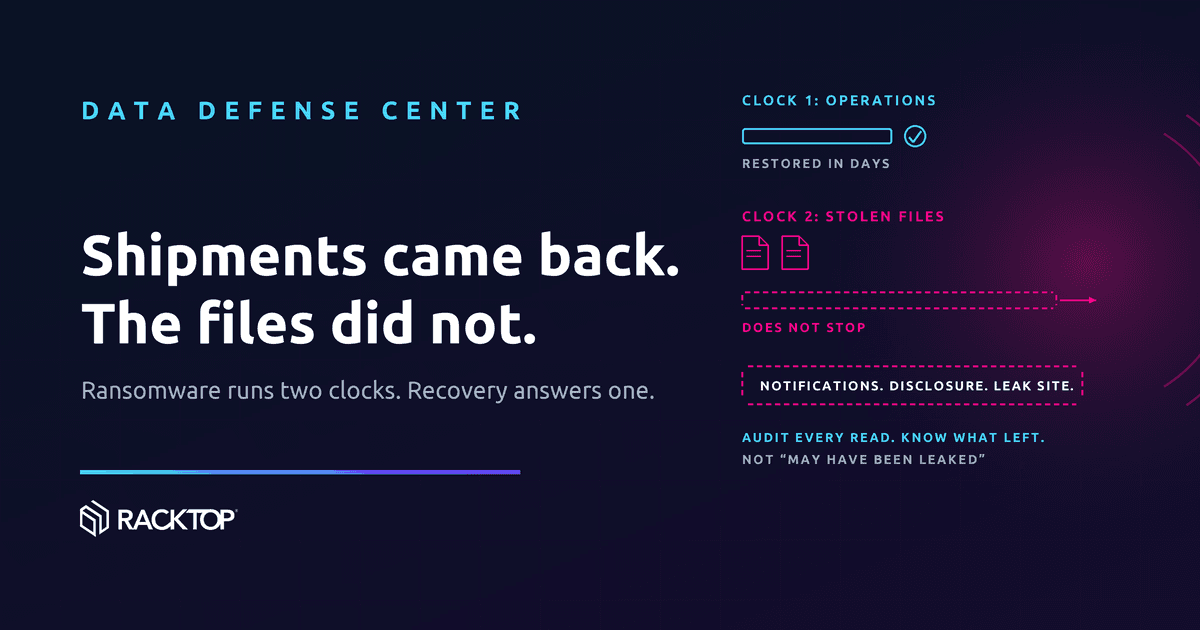
Nichirei and the second clock: shipments came back, the files did not
A ransomware crew claims it took internal files from Japanese frozen-food and logistics company Nichirei and reportedly posted samples as proof. Deliveries were restored within about a week. The company was still notifying people whose personal information may have been exposed.
5 min read
Backup is necessary. It is not a security control.
Immutable backups matter. But a recovery copy cannot see an attack, cannot stop exfiltration, and cannot tell you that data was stolen. Treating backup as security leaves the live data undefended.
5 min read
Ransomware protection at the storage layer: how it actually works
What real ransomware protection looks like at the layer attacks actually touch: the visibility, detection, policy, response, recovery, and evidence chain, explained link by link.
9 min read
A government paid $1 million to Kairos — and the blockchain shows it recovered nothing
Fresh analysis this week traces a roughly $1 million extortion payment from a U.S. government entity to the Kairos group, for data that was never encrypted, only stolen. The payment is visible on the blockchain. The files were taken anyway.
5 min read
Extortion without encryption: the steal-and-leak business model
A growing share of extortion groups no longer bother encrypting anything. They steal files and threaten to publish them, a model that makes backups irrelevant and puts all the weight on stopping the theft itself.
2 min read
Recovery time is now a disclosure question
Regulators, insurers, and customers increasingly ask the same two questions after an incident: how fast were you back, and what exactly was taken? Both answers are determined at the data layer, before the incident ever happens.
2 min read
A board-level view of unstructured data risk
Most of an organization’s data is unstructured files, and most of its risk concentrates there. A short briefing for executives on why the storage layer belongs on the risk register.
2 min read
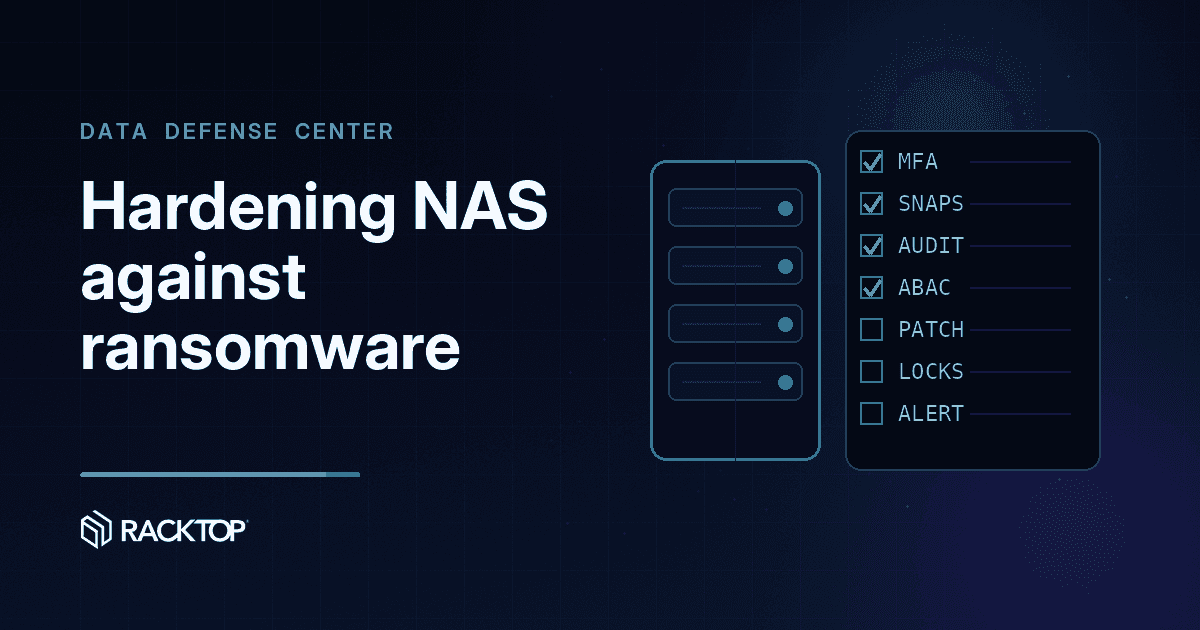
Hardening NAS against ransomware: a practitioner checklist
A working checklist for storage and security teams: seven areas to verify on your file infrastructure so an attack on a share is detected and contained in progress, not just recovered from later.
5 min read
See data-layer defense in your environment
In a 30-minute demo we’ll show Active Defense stopping an attack inline, immutable recovery, and surgical rollback — mapped to your data and your threats.