7 articles
Practitioner Guides
Hands-on guidance for storage, security, and SOC teams: NAS hardening checklists, file activity telemetry for the SOC, and behavior-based ransomware defense.
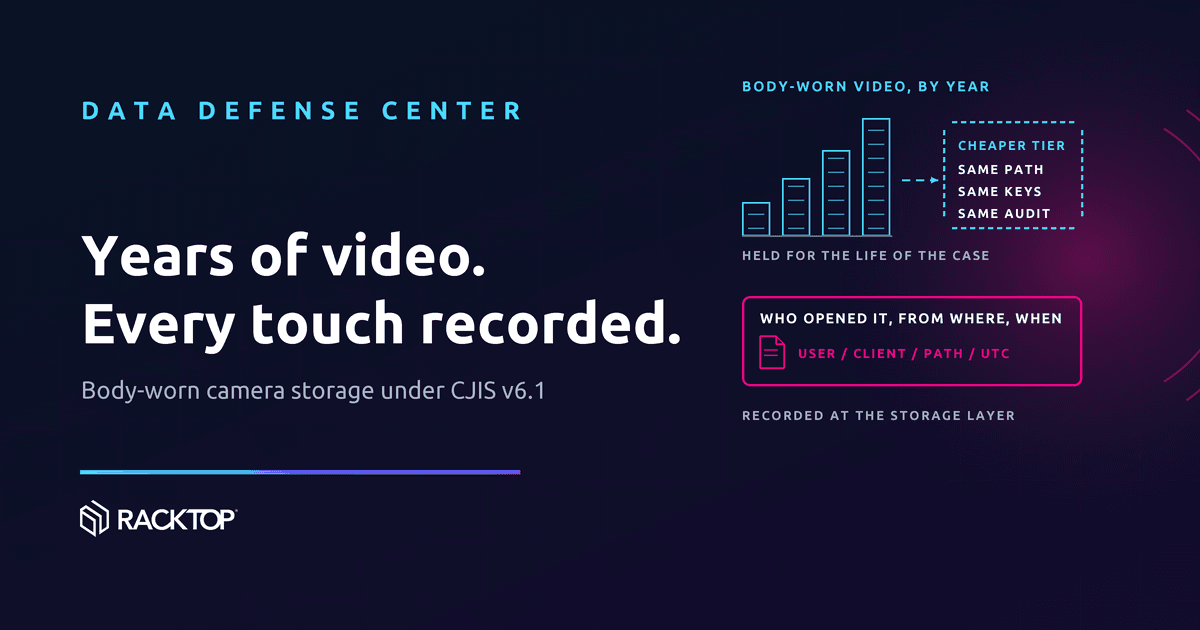
Body-worn camera storage: retention, chain of custody, and CJIS
Body-worn camera video is the largest and fastest-growing data set most departments own. Here is how to store it for years, prove who touched each file, keep it inside CJIS controls, and get it back after a ransomware attack.
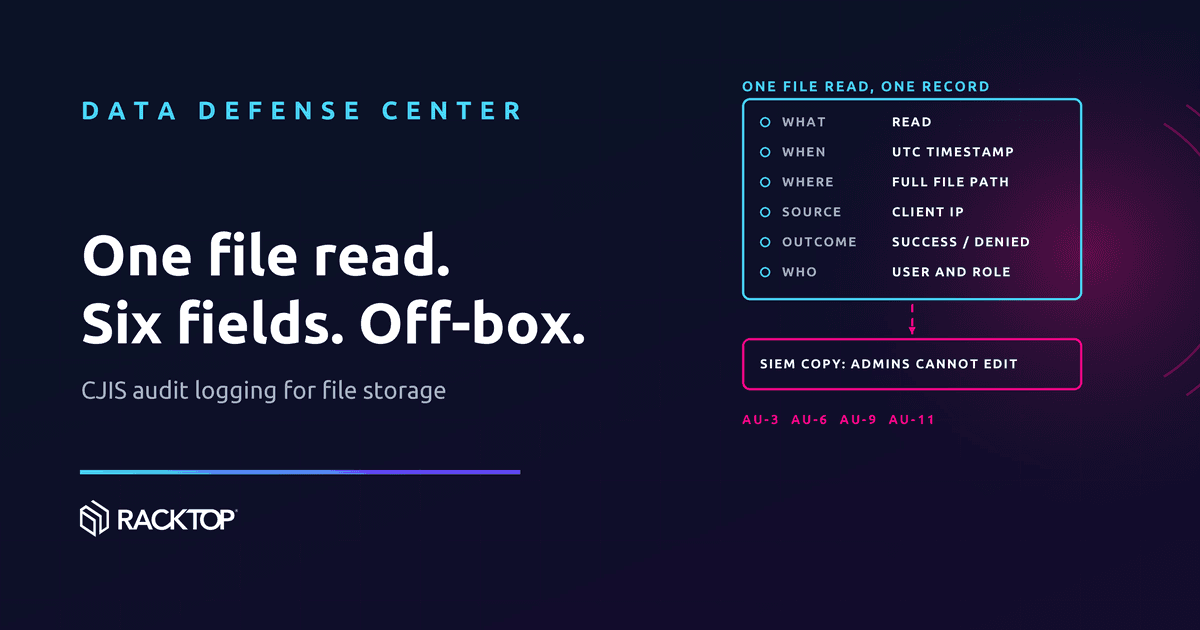
CJIS audit logging requirements for file storage
The CJIS audit controls read directly against the storage holding CJI. Here is what each one asks for, what an auditor will want to see, and where file shares usually fall short.
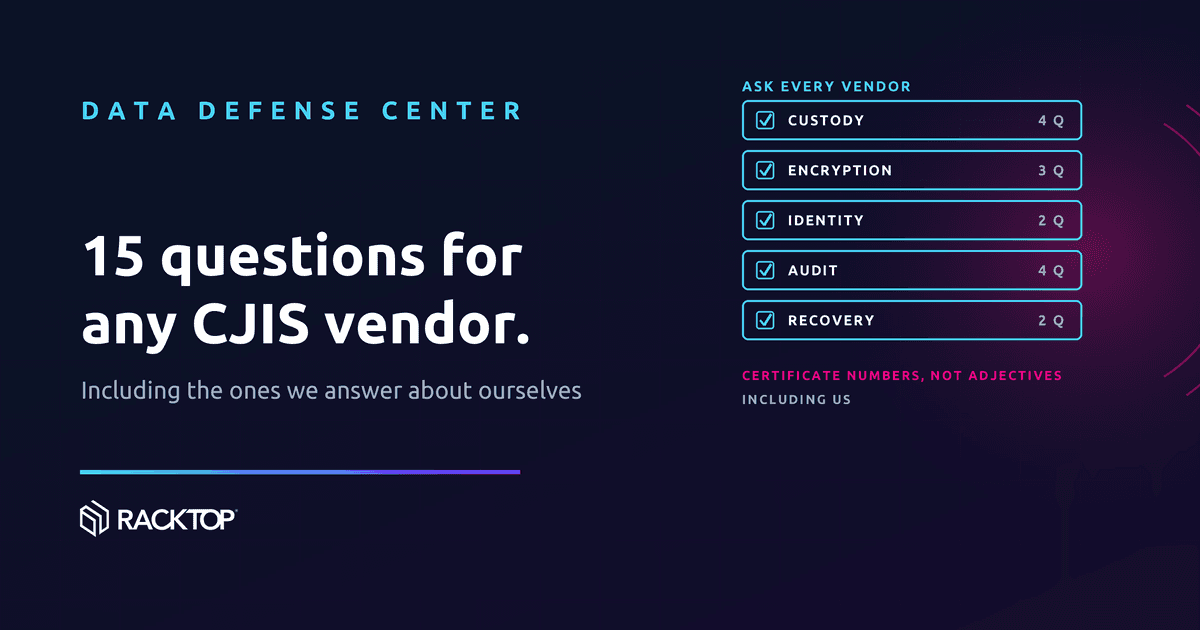
CJIS storage checklist: 15 questions for any vendor holding your CJI
No storage product is CJIS certified, so a vendor’s CJIS page tells you little. These fifteen questions turn the CJIS v6.1 controls into answers you can check, and we answer every one of them for BrickStor SP.

When every storage product claims Cyberstorage: seven tests that tell them apart
Gartner expects every storage product to include Cyberstorage capabilities by 2029. When the label is universal, a datasheet stops telling buyers anything. Seven live tests for a proof of concept still can.
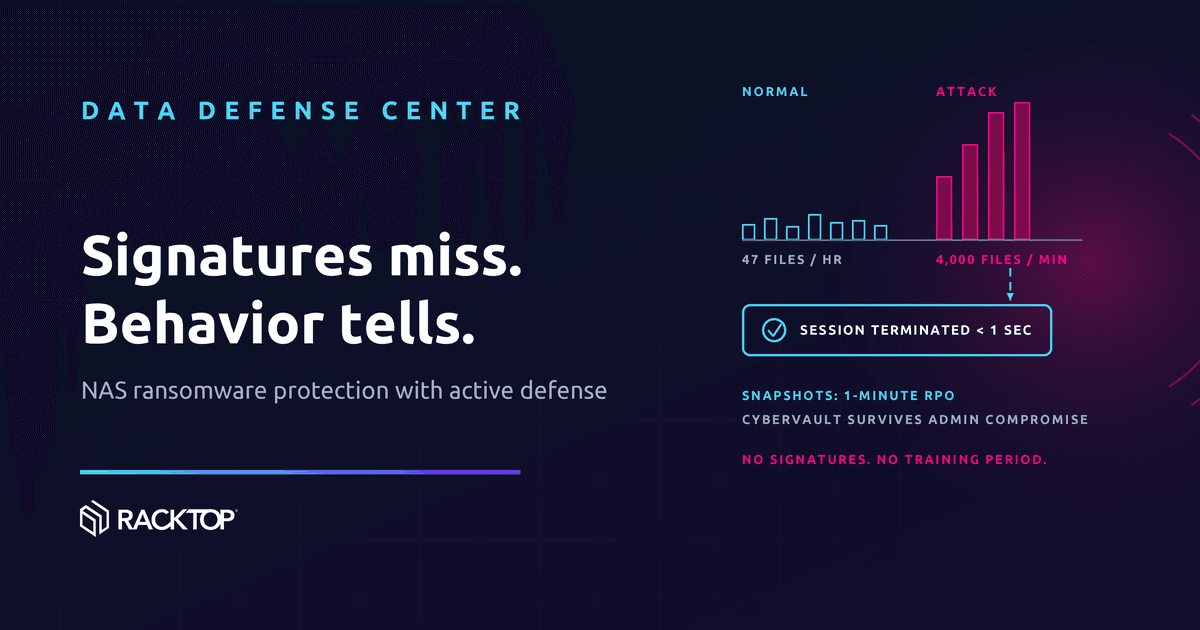
NAS ransomware protection: catch the attack by how it behaves
Real NAS ransomware protection is not a signature list or a nightly backup. It is user behavior analytics on every file operation, active defense that terminates a hostile session in under a second, and a cybervault that survives even administrative compromise.
File activity telemetry: what your SOC actually needs from storage
Most NAS audit feeds were designed for compliance checkboxes, not threat detection. Here is what detection-grade file activity telemetry looks like, how to wire it into SIEM and SOAR workflows without drowning the license, and the two tests that prove the integration is real.
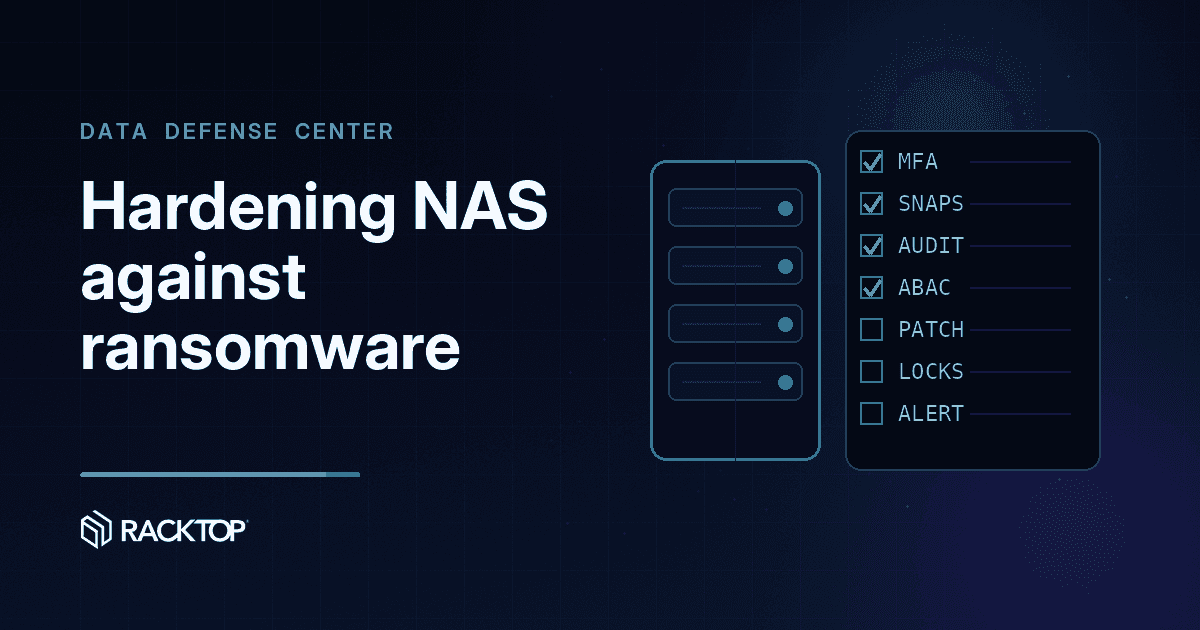
Hardening NAS against ransomware: a practitioner checklist
A working checklist for storage and security teams: seven areas to verify on your file infrastructure so an attack on a share is detected and contained in progress, not just recovered from later.
See data-layer defense in your environment
In a 30-minute demo we’ll show Active Defense stopping an attack inline, immutable recovery, and surgical rollback — mapped to your data and your threats.